How PODremit™ is rethinking authorization, trust and changing human roles
The Trust Problem Is Not Simply “Will the Money Arrive?”
In a three-party support transaction, arrival is only one part of trust. The payer wants to know which merchant is being paid and for what purpose. The recipient wants the need to be understood without losing dignity or control of their own information. The merchant wants confidence that the authorization is valid and connected to the correct transaction.
Traditional person-to-person transfers are useful when flexible cash is the goal. But when everyone intends a specific school, hospital or merchant to receive payment, an unrestricted transfer can leave important information outside the payment itself. Messages, screenshots and verbal assurances become a separate layer of coordination.
PODremit™ is being designed to bring that coordination into the product experience.
A Three-Participant Model
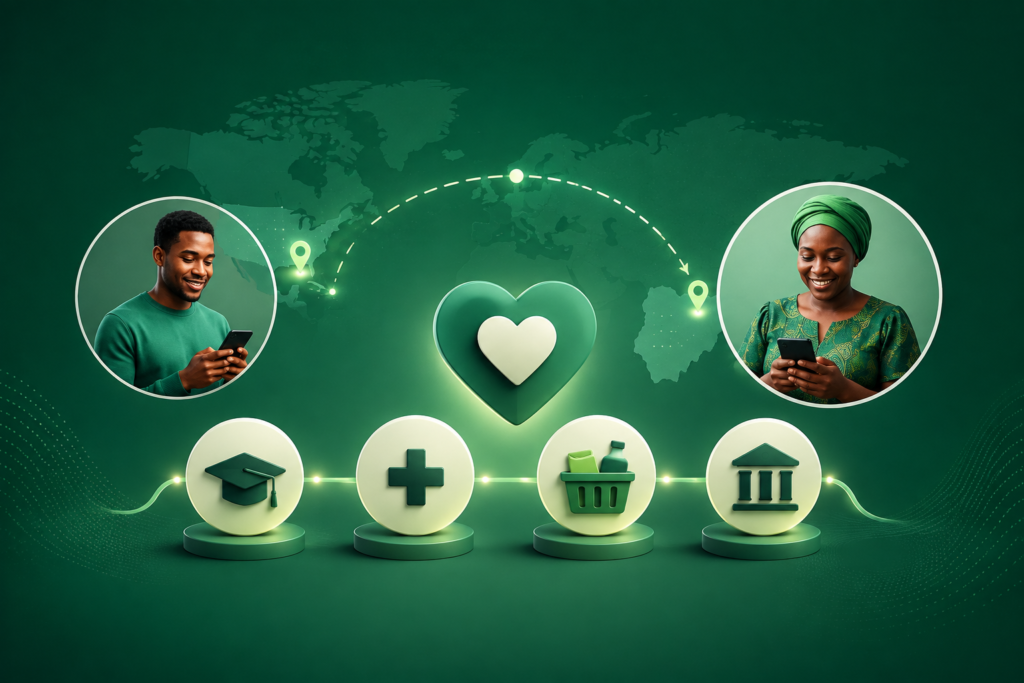
The PODremit™ model begins with three participants: payer, recipient and merchant. Each plays a different role in a shared purpose.
The payer supplies the funds and holds final authorization authority. The recipient is the person whose education, healthcare or essential need is being supported. The merchant is the school, provider or business selected to fulfill that need.
Either the payer or the recipient may initiate the process. A payer can choose a merchant and prepare support directly. A recipient can identify the merchant and submit a request. In the second case, the payer reviews the request before deciding whether to authorize it. A request communicates a need; it does not move the payer’s money.
The Secure Authorization Token Explained
The Secure Authorization Token, or SAT, is the planned digital object representing the payer’s approved instruction. It may contain or reference the merchant, approved amount, currency, purpose, validity period, status and other controls required by the final implementation.
A SAT is not cash and cannot be understood as a general stored balance. It is not a bank account, wallet or escrow account. Its purpose is to make the authorization specific, traceable and usable within the designed transaction flow.
The token concept allows the platform to distinguish among a request awaiting approval, an active authorization, a merchant interaction, a completed payment, an expired authorization, a decline, a dispute or another defined state. The precise technical and legal implementation will continue to evolve.
Why One SAT Is Connected to One Merchant
PODremit™’s current policy is one SAT per merchant. If a recipient needs tuition paid to a school and books purchased from a separate merchant, those needs should not be collapsed into one ambiguous authorization. Separate merchant-specific SATs can preserve the approved amount and purpose for each destination.
A multi-merchant request may still appear to the participants as one coordinated need, while the system manages separate child authorizations beneath it. The parent structure can remain internal rather than confusing users with unnecessary technical detail.
This design supports clearer merchant boundaries, transaction monitoring, reconciliation and confirmations. It also limits the risk that an authorization intended for one merchant could be presented elsewhere.
Split Support Without Blurred Authority
Some needs may be too large for one person to cover. PODremit™’s planned request flow includes the possibility of split support, allowing more than one payer to contribute toward an identified need.
Each payer should authorize only their own contribution. The product must preserve who approved what amount, for which merchant and under which transaction. No participant should be able to extend another payer’s authorization.
This is an example of how a simple social reality—families often share responsibility—creates sophisticated product requirements. Properly designed, split support could make collaboration easier without weakening consent or traceability.
Role Interchangeability Reflects Real Life
A person is not permanently a payer or recipient. The same user who supports a parent’s medical need may later request help with a child’s tuition. Role interchangeability allows the consumer experience to reflect that change without requiring separate accounts or identities.
The system still needs clear permissions. The active role must be visible, records must show who initiated and who approved, and merchant functions must remain within the merchant environment. Flexibility is not the absence of boundaries; it is the ability to change roles while preserving them.
This concept may become one of PODremit™’s most defensible contributions because it joins human behavior to authorization architecture.
Trust Requires Records, Notifications and Exceptions
A token alone does not create trust. The surrounding system must make important events visible. PODremit™’s planned design includes notifications and confirmations for payer, recipient and merchant; transaction histories; authorization-state tracking; merchant and identity verification; monitoring; administrative controls; dispute handling and audit logs.
These capabilities must account for failure as well as success. An authorization may expire. A merchant interaction may fail. A payer may decline a request. A transaction may require review. The system should communicate each state accurately rather than presenting every journey as inevitable completion.
Trust grows when users can understand both the normal flow and the exception path.
How the Model Could Operate in the Future
PODremit™ is intended to function as a technology and orchestration layer connected to regulated payment providers rather than as a substitute for banks, licensed transmitters or settlement networks. The final division of responsibilities will depend on legal analysis, partner arrangements and technical implementation.
The first controlled pilot is proposed for education payments in the United States–Nigeria corridor, followed later by healthcare and essential needs. That pilot should test whether people understand the three-party model, whether merchant-specific authorization works in practice and whether the operational controls support a reliable experience.
The goal is not to claim that technology can guarantee trust. It is to give trust a clearer structure: an identified purpose, explicit authorization, defined participants and a visible record of what happens next.